
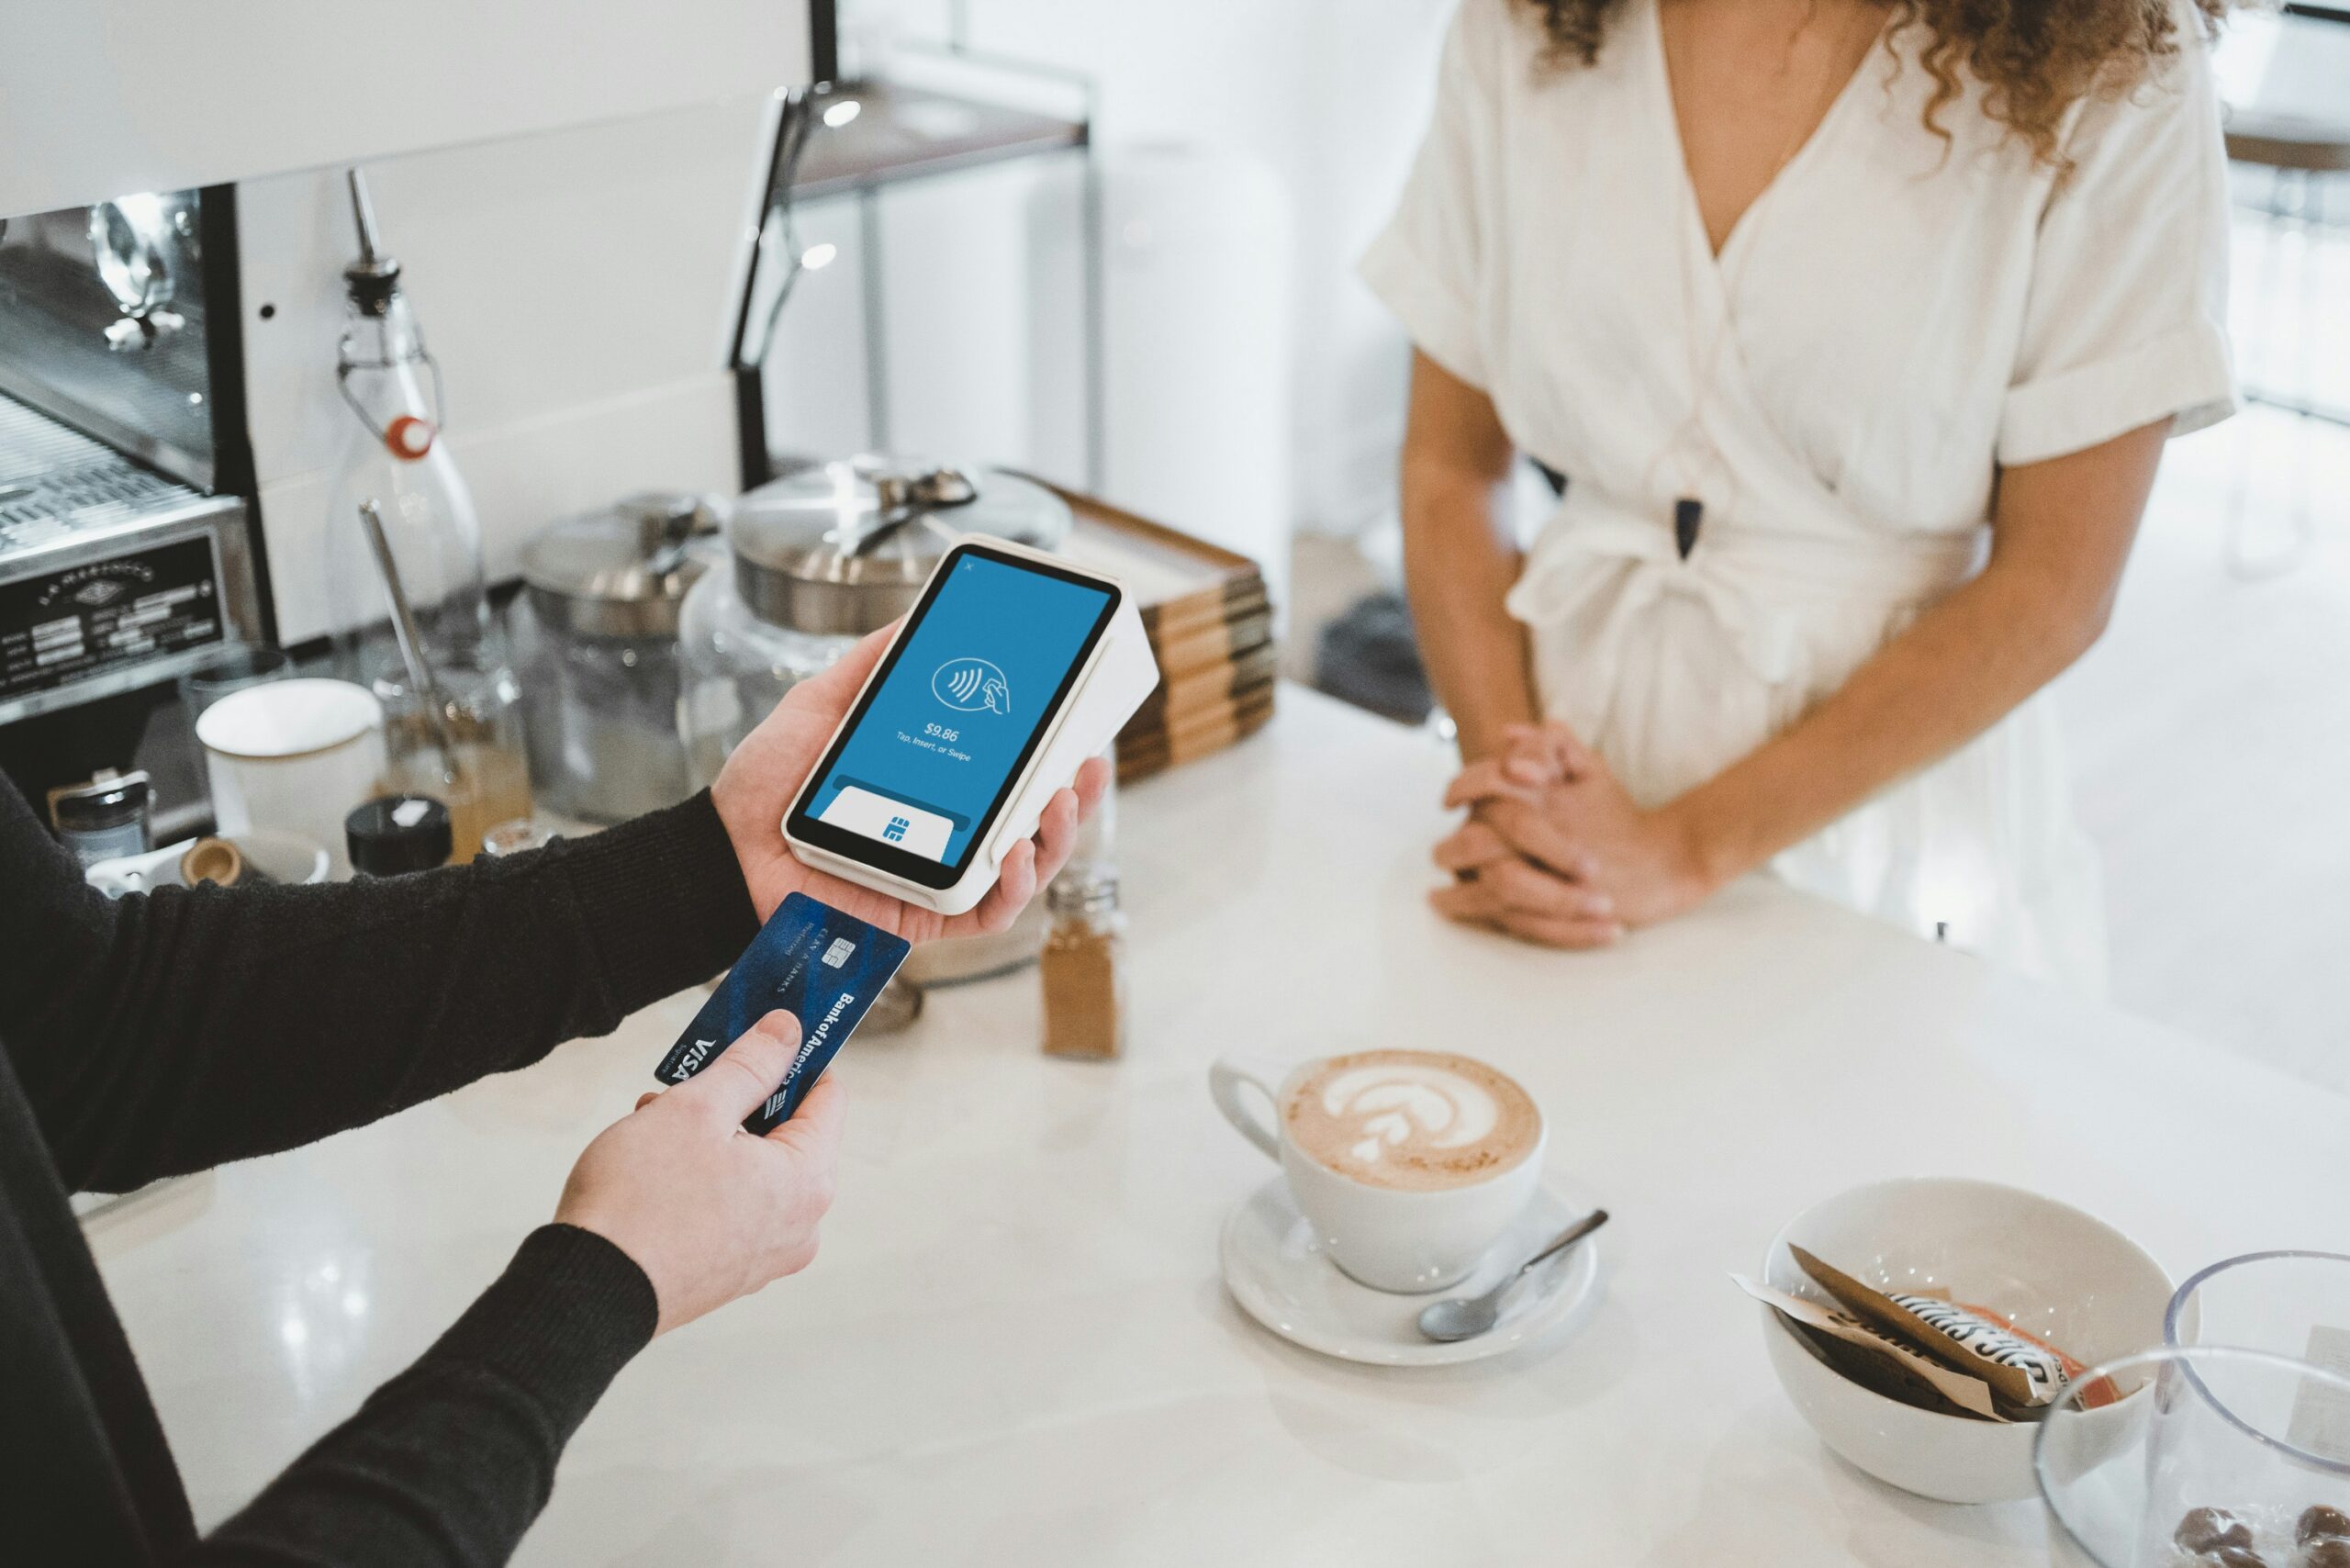
India’s and China’s payment authorities, alongside Visa, Mastercard and Ant International, have each moved in recent weeks to build systems for identifying and authorizing AI agents that pay on people’s behalf, as far as we can see from the sources we reviewed. None of the three efforts yet says who is liable when an agent gets it wrong.
A registry sounds like a filing cabinet. What India, China and the world’s largest card networks are actually building this September, as far as we can see from the sources we reviewed, is closer to a set of border checkpoints going up simultaneously along three different borders, each with its own passport format, and no shared customs union yet in sight.
India’s National Payments Corporation of India, which runs UPI, the world’s largest retail fast-payment network by transaction volume, is building an AI agent registry as part of a planned Unified Agentic Protocol.
In China, the Payment & Clearing Association of China, operating under the guidance of the People’s Bank of China, has released a self-discipline convention that introduces its own “know your agent” mechanism.
And Ant International, the Singapore- and Shanghai-based digital-payments arm of Alipay’s parent group, has begun a Know-Your-Agent interoperability effort with Visa and Mastercard aimed at recognizing trusted agents across card and wallet networks. Three checkpoints.
Three formats. No union.
What Each System Actually Checks
India’s approach starts small, on purpose. Groceries. Low-value, frequent, forgettable purchases.
NPCI chairman Ajay Kumar Choudhary told the Global Fintech Fest that the architecture will separate intent, authorization, and settlement into distinct layers, with an AI system permitted to interpret what a user wants while the final settlement layer stays rule-based and legally final.
China’s convention reads more like a rulebook than a rollout: a know-your-agent mechanism modeled on know-your-customer standards, tiered risk controls, transaction limits, and, notably, a requirement that member institutions report to the association and clear an ethics-and-security review before any agent is allowed to initiate a payment on its own.
Neither system, as far as the sources we reviewed say, has published how it would treat an agent authorized in one country transacting through infrastructure built for the other.
The Trust Gap Behind the Trillion-Dollar Bet
Ant International, Mastercard and Visa project that AI agents will orchestrate US$3 trillion to $5 trillion of global consumer commerce by 2030.
Visa’s own newly released Trust Index, fielded by the Harris Poll among just over 2,000 US consumers in late May, found that only 23% of respondents trust GenAI generally to handle a payment transaction on their behalf, a figure that rises to 61% when the question is specifically about trusting Visa to do it.
Mastercard, in a separate report published this month, argues that the future of commerce “will not be defined by the smartest agents or the fastest transactions” but “by the systems people trust enough to delegate to,” a framing that reads less like caution and more like a company narrating the very trust gap it is trying to close.
The same report is not purely aspirational on that point: it dates Europe’s first end-to-end agentic payment transaction, completed by Mastercard with Worldline and ING at Money20/20 in 2026, suggesting at least one live transaction sits behind the messaging, not just a projection.
Read plainly, the companies appear to be projecting trillions in volume onto a consumer base that, per their own numbers, does not yet trust the underlying technology, only the brand wrapped around it and, in a few documented cases, the rail itself.
The More Salient, Unanswered Question
Every one of these systems, India’s registry, China’s convention, the Visa-Mastercard-Ant collaboration, is built to answer one question: is this agent who it says it is. None of them, as far as we can see from the sources we reviewed, fully answers a second, harder question: what happens when the agent it correctly identified still does the wrong thing.
PBOC Deputy Governor Lu Lei, speaking at an industry forum reported by Caixin, warned that excessive AI autonomy could erode trust, because current governance assumes a human is still the one deciding.
India’s sources told Reuters that liability for wrong or unauthorized payments “will need to be addressed through regulation,” without saying how.
It isn’t, not yet, though it is at least being sketched: Mastercard’s own report predicts that by 2030 every agentic transaction will carry “an embedded, machine-readable liability warranty” pricing the risk of a misbehaving agent before the purchase ever completes.
That is a proposal from one of the companies building the infrastructure, not a deployed standard, and it answers Lu Lei’s warning only on paper so far. Whether it holds up once an agent actually gets it wrong is still an open question.
The is the Same Governance Lag, Applied to Money
This is the fourth time this year I’ve watched the same thing happen in a different room. A capability gets built and deployed at speed, and then the system to govern it gets built after, in pieces, by whoever’s standing closest to the money or the liability when it goes wrong.
I saw it in AI budgets. I watched it happen to AI lab oversight. Then to breach accountability. Now it’s happening to payments.
“Trust Me, Bro”
I reported in August that AI labs keep outsourcing AI oversight — routing safety review to partners, or to the model itself, rather than strengthening it in-house. The pattern repeats here almost exactly.
Mastercard’s trust research and Mastercard’s liability-warranty proposal appear in the same report, authored by the same company, describing a gap that company also stands to profit from closing. That confidence is real, even and especially because it’s self-reported.
It’s not evidence the fix works. It’s evidence of who’s currently allowed to propose one.
Three Checkpoints Don’t Make a System
Three registries. Three formats. No shared customs union. I’ve called this exact failure “capability without visibility” before, in enterprise AI spend: systems that scale faster than anyone’s ability to see what they’re doing, in several places at once, none of them talking to each other.
India’s registry, China’s convention, the Visa-Mastercard-Ant effort; same failure, in the domain of payment rails instead of workspace tools.
We’ve been here too: my story on three labs, four breaches found California’s AB 316 stating outright that software isn’t the liable party, without saying who is. Lu Lei’s warning is the payments version of that same unfinished sentence.
Aklatan’s news and analysis drills down to the structural mechanics, geopolitical shifts, and hidden constraints truly driving AI and Asian tech ecosystems and knowledge work.
See coverage span here: Aklatan’s News and Analysis
Generative AI Transparency:
This article was written primarily with generative AI, specifically SupraGraphos’ A.C.E. News Module. Reviewed with human post-editing, all sources and claims are confirmed as of the time of writing.